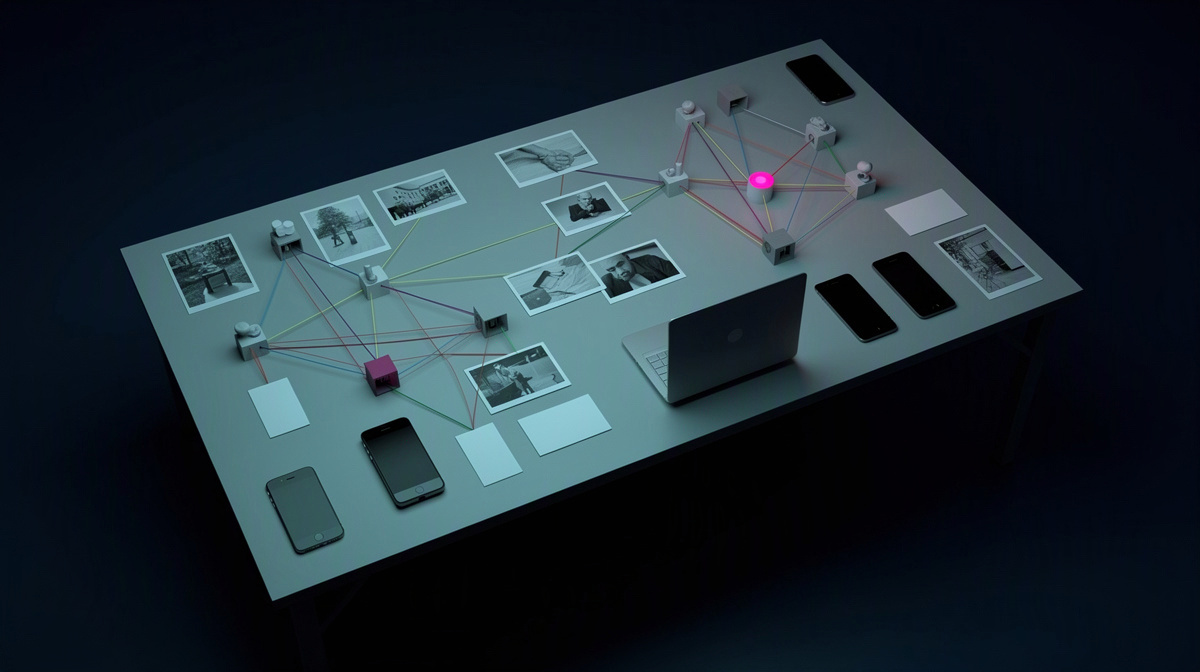
Entity resolution is the work of deciding, in plain investigative terms, when separate records likely point to the same scam actor. For threat-intelligence and trust-and-safety teams, that means judging whether different chats, accounts, payment details, files, or images belong together as one operational picture. This article explains what entity resolution is, why it matters in scam investigations, what kinds of evidence usually support or weaken a link, where the process fails, and how to make it useful in an intelligence workflow. The goal is not simple deduplication. It is building a defensible actor-level view from partial, noisy, and changing evidence, with practical investigation use in mind.
What Entity Resolution Means in Scam Work
In scam investigations, entity resolution means linking records that may refer to the same real-world actor, account set, or operation even when the visible names and identifiers do not match. A wallet can change, a handle can be replaced, and a new contact point can appear, while the underlying scam activity remains connected.
That is why this work is noisy. Scam actors rotate accounts, reuse assets selectively, forward messages between accounts, and change contact points over time. One conversation may expose a payment detail, another a messenger account, and a third a reused image. Analysts are trying to decide whether those fragments belong to one operational picture.
For threat-intelligence and trust-and-safety teams, the main unit of interest is usually not a legal identity. It is an operational actor or scam cluster that can be tracked, blocked, escalated, or monitored. In practice, that means building links that are useful for disruption and investigation, even when the person behind them is still unknown.
Some links come from exact matches. The same phone number, wallet, or file hash appearing again is direct evidence. Other links are probabilistic: they do not prove a match on their own, but they raise or lower confidence when seen with other signals. More on that is covered in how shared indicators support linkage.
Analysts care about precision and traceability because bad merges can contaminate cases, while missed links leave networks fragmented. The usual evidence groups include:
- communications identifiers
- payment identifiers
- infrastructure
- media artifacts
The Evidence That Supports or Weakens a Link
Entity resolution stands or falls on the evidence in hand and the confidence attached to each item. In scam work, the question is not just whether two records share something, but how much that shared detail should matter.
Active Defense turns scam conversations into intelligence that includes:
- crypto wallets
- bank details
- phone numbers
- messenger accounts
- links
- gift cards
- payment handles
- file hashes
- photo hashes
Each indicator is scored with a confidence score. That gives analysts a way to decide whether a proposed link should be trusted, sent for review, or held back until more support appears. For example, a directly reused wallet or bank detail often carries more weight than a disposable username, though context can shift the meaning of both. More on wallet evidence is covered in wallet evidence in scam cases, and bank-account context in bank-account context for investigators.
Media can also be highly useful for linkage. The same photo or file may reappear across separate chats even when handles, phone numbers, or payment requests change. That is one reason file and photo hashes matter: they preserve a comparison point when visible identifiers are rotated. Related examples of account-level linkage are discussed in account-level linkage work.
In Active Defense, chats that share an indicator, a reused photo, or a forwarded account are linked to one actor. That turns isolated chats into an actor view built from evidence that analysts can inspect.
That last point matters. Confidence-scored evidence should be presented as something analysts can examine, not as a black box conclusion. Investigators often combine machine support with analyst review because the same data point can be benign in one case and highly probative in another, especially with gift cards or payment handles. One example is gift-card payment signals.
Why Message History and Timing Matter
Entity resolution gets stronger when evidence is preserved at arrival time. In scam investigations, visible traces often change after the fact: messages are deleted, payment details are removed, media disappears, and account references are edited or replaced. If an analyst only sees the latest state, an important link may already be gone.
Active Defense stores every message the moment it arrives, so a scammer’s later "delete for everyone" does not remove the copy. That matters because a deleted message may have contained the payment request, contact detail, forwarded account, or image that connected one chat to another. Related background is covered in why scammers delete messages.
Point-in-time preservation also helps analysts reconstruct what was known when. A weak clue in one conversation may not mean much during first triage, then become important later when another chat surfaces the same wallet, file, or account. Preserved history makes it possible to revisit that earlier evidence in context instead of relying on a partial snapshot.
This is why event-level history matters more than only keeping the latest visible state. Edits, deletions, forwarded content, and reused artifacts can all reveal behavior patterns that are useful for linkage. Media retention is part of that picture as well: when the same file or image appears again in a separate conversation, the retained copy supports later comparison.
For analysts, preserved history is useful in two directions:
- current triage, when deciding whether a new chat should be linked or held back
- retrospective analysis, when a later conversation gives earlier evidence new meaning
From Collected Chats to an Analyst-Usable Feed
Entity resolution becomes operationally useful when linked evidence can move into the systems analysts already use for enrichment, triage, and case building. If the result stays trapped in chat transcripts, teams spend time copying details by hand and risk losing the relationship between the indicator and the conversation that gave it meaning.
Active Defense runs AI decoy personas on Telegram and by e-mail to keep scammers talking and turn what they hand over into a threat-intelligence feed. Replies are drafted by AI and approved by a human operator by default, which matters for readers who care about collection quality and oversight.
At a high level, the output is actor-linked scam indicators derived from live conversations, suitable for fraud, trust-and-safety, and intelligence workflows. Each customer gets their own feed with STIX 2.1 export. For teams planning ingestion and internal sharing, it helps to think in terms of structured scam indicator feeds, not isolated chat screenshots.
A structured feed matters because it helps teams:
- ingest indicators into existing workflows
- preserve relationships between chats, indicators, and linked actors
- share findings internally without manually copying from conversations
- revisit earlier evidence as new linked chats appear
That relationship layer is the real value. Entity resolution is not only about finding one more wallet, account, link, or file hash. It is about preserving how those items relate to one another and to the actor or conversation context that makes them useful in analysis.
For that reason, export format matters as much as collection. A feed that preserves linked evidence is easier to use in downstream systems and easier to review later. More detail on that is in using STIX 2.1 for scam indicator feeds.
Limits, Failure Modes, and Review Standards
Entity resolution works best when teams set review standards before they start linking. The point is not to force every record into a cluster. It is to keep uncertain links visible, separate, and explainable until more evidence arrives.
A practical review standard usually asks:
- what exact artifacts support the link
- whether the support is direct or circumstantial
- how much conflicting evidence exists
- what action, if any, the link is strong enough to support
That matters because scam data is messy in ways that do not fit one fixed threshold. A shared bank detail may deserve fast attention. A reused photo may need more context. A forwarded account can be useful, but its meaning depends on how it appears across conversations.
Review should also distinguish collection from judgment. Active Defense gathers indicators from scam conversations, scores them, and links chats that share an indicator, a reused photo, or a forwarded account. Analysts still need a standard for when a proposed actor link is accepted, left tentative, or split apart later.
Teams usually calibrate that standard over time by comparing current cases with patterns seen in weekly scam briefings and monthly scam data reports. That helps keep decisions consistent across triage, investigations, and escalation without treating every scored link as equally reliable.
Questions analysts ask about entity resolution
What does entity resolution add beyond matching exact fields?
It helps analysts work with partial overlap instead of waiting for perfect repetition. In scam cases, one chat may expose a wallet, another a bank detail, and another a messenger account or reused image. Entity resolution asks whether those records should stay separate or be handled as one investigation target.
For analysts, the practical output is usually a working actor cluster, not a confirmed civil identity. That makes the method useful for triage, monitoring, and handoff.
When should two scam records stay separate?
They should stay separate when the overlap is thin, conflicting, or too common to mean much on its own. A single low-value shared detail can create bad merges if teams treat every match as equally important.
Common reasons to hold back include:
- one shared detail with weak context
- conflicting payment or contact patterns
- indicators scored too low for action
- no second signal to support the link
A temporary split is often better than forcing an early merge that later contaminates review.
What should analysts expect from tooling that supports entity resolution?
Tooling should make the basis for a link easy to inspect. In Active Defense, every message is stored the moment it arrives, indicators from scam conversations are scored, and chats that share an indicator, a reused photo, or a forwarded account are linked to one actor.
The collection side also matters. Active Defense runs AI decoy personas on Telegram and by e-mail, with replies drafted by AI and approved by a human operator by default. Each customer gets their own feed with STIX 2.1 export, so linked records can move into analyst workflows without rebuilding the chain of evidence by hand.
Turning Entity Resolution Into Actionable Scam Intelligence
For teams searching for entity resolution that leads to action, the next step is to test whether linked scam records fit real analyst workflows. On the Active Defense home page, qualified leads can request a free feed sample or start a 90-day pilot for up to 500 conversations at 1,900 EUR net, credited to the subscription afterwards.
That gives analysts a practical way to assess output before wider rollout.